
HiltonC
Most industrial facilities have an emergency response plan. Very few have one that actually works under pressure. The difference is not the thickness of the binder or the number of signatures on the cover page — it is whether the plan was engineered into the facility’s systems from the beginning, or assembled after the fact to satisfy a regulatory checkbox.
In process facilities — refineries, petrochemical plants, LNG terminals, industrial manufacturing — an emergency response plan (ERP) is not a standalone document. It is an engineering deliverable. It must be tightly integrated with the fire detection architecture, the suppression system logic, the emergency shutdown (ESD) sequence, the site layout, and the coordination protocols with external responders including Saudi Civil Defense. When those connections are missing, the plan creates false confidence. When they are present and tested, the plan compresses response time and saves lives and assets.
This article outlines what an engineered ERP looks like, what it must connect to, and where most Saudi and international industrial operators fall short.
Why Most Emergency Response Plans Fail in Practice
The most common failure is not inaccuracy — it is disconnection. Facilities develop ERPs in isolation, often by HSE teams working from templates, without systematic input from the engineers who designed the fire detection, suppression, and ESD systems. The result is a plan that describes the right general sequence but contains none of the specific operational logic the site actually needs.
A second failure mode is static documentation. Process facilities are not static environments. Equipment is added, process streams are modified, storage configurations change, and staffing levels shift between shifts and seasons. An ERP that was accurate at commissioning may be dangerously misleading two years later if it has not been updated to reflect those changes — and most are not. NFPA standards and Saudi Civil Defense requirements both address the necessity of periodic plan review and revision, but compliance on paper does not guarantee operational currency.
A third failure is the assumption that the plan will be read and executed under stress by people who have rarely or never practiced it. Emergency conditions generate cognitive load, communication breakdown, and decision paralysis. A plan that requires personnel to locate information, interpret diagrams, or make judgment calls in the first minutes of a major fire is a plan written for normal conditions, not emergency ones. Effective ERPs are engineered for speed — they encode the critical first actions into pre-defined roles, automated system responses, and practiced drills, not into text that someone has to read while the alarm is sounding.
The Engineering Inputs an ERP Must Be Built From
An effective emergency response plan for a process facility is not drafted — it is derived. It starts with the engineering baseline that already exists for the facility and makes that baseline operationally useful under emergency conditions.
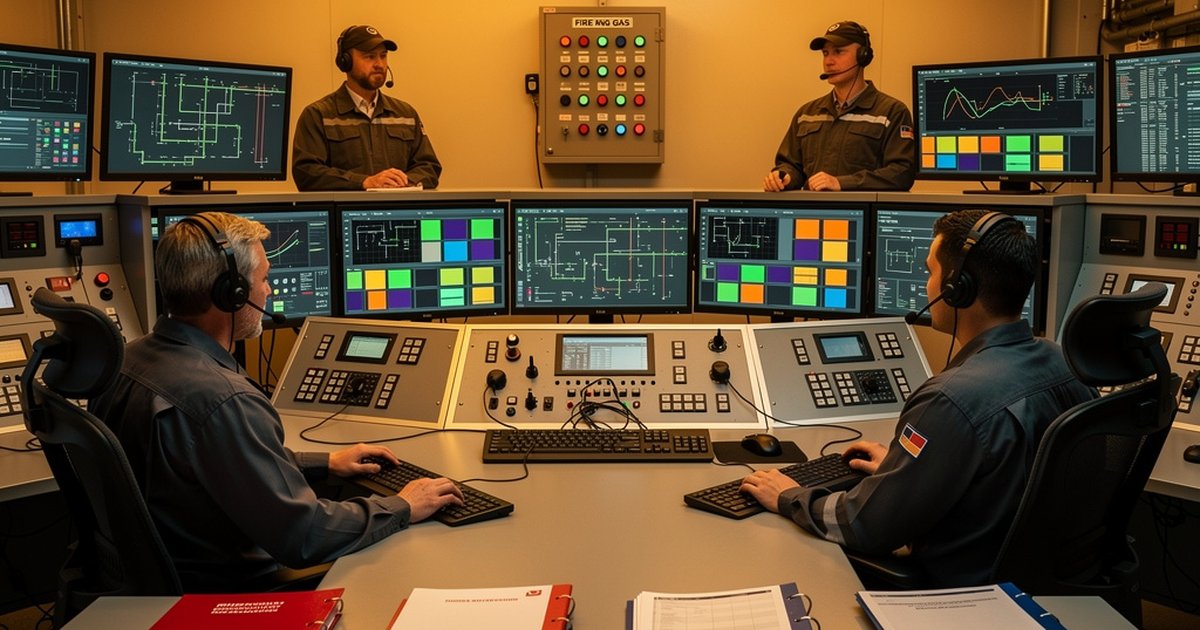
Fire and gas detection architecture. The ERP must be built around the actual detection system: where the detectors are, what they detect, what alarms they trigger, and what automatic actions follow. Every zone in the facility should have a defined detection-to-action sequence documented in the plan, including the expected time from alarm to suppression activation and the personnel actions required in parallel. Plans that describe generic detector placement or reference a “fire detection system” without specificity give responders nothing useful.
Suppression system logic and coverage. Operators responding to a fire need to know which suppression system covers the affected area, whether it activates automatically or requires manual initiation, where the local isolation and override controls are, and what the water supply situation looks like under simultaneous demand. This requires the ERP author to have read and understood the hydraulic design, the system zoning drawings, and the sequencing logic — not just the equipment list.
Emergency shutdown sequence. In process facilities, fire response is inseparable from process isolation. The ERP must define the ESD activation logic, including which process streams shut down in which order, what the depressurization or blowdown sequence is, and how those actions interact with the suppression systems. Getting this sequence wrong — or failing to execute it at all — can intensify a fire rather than control it.
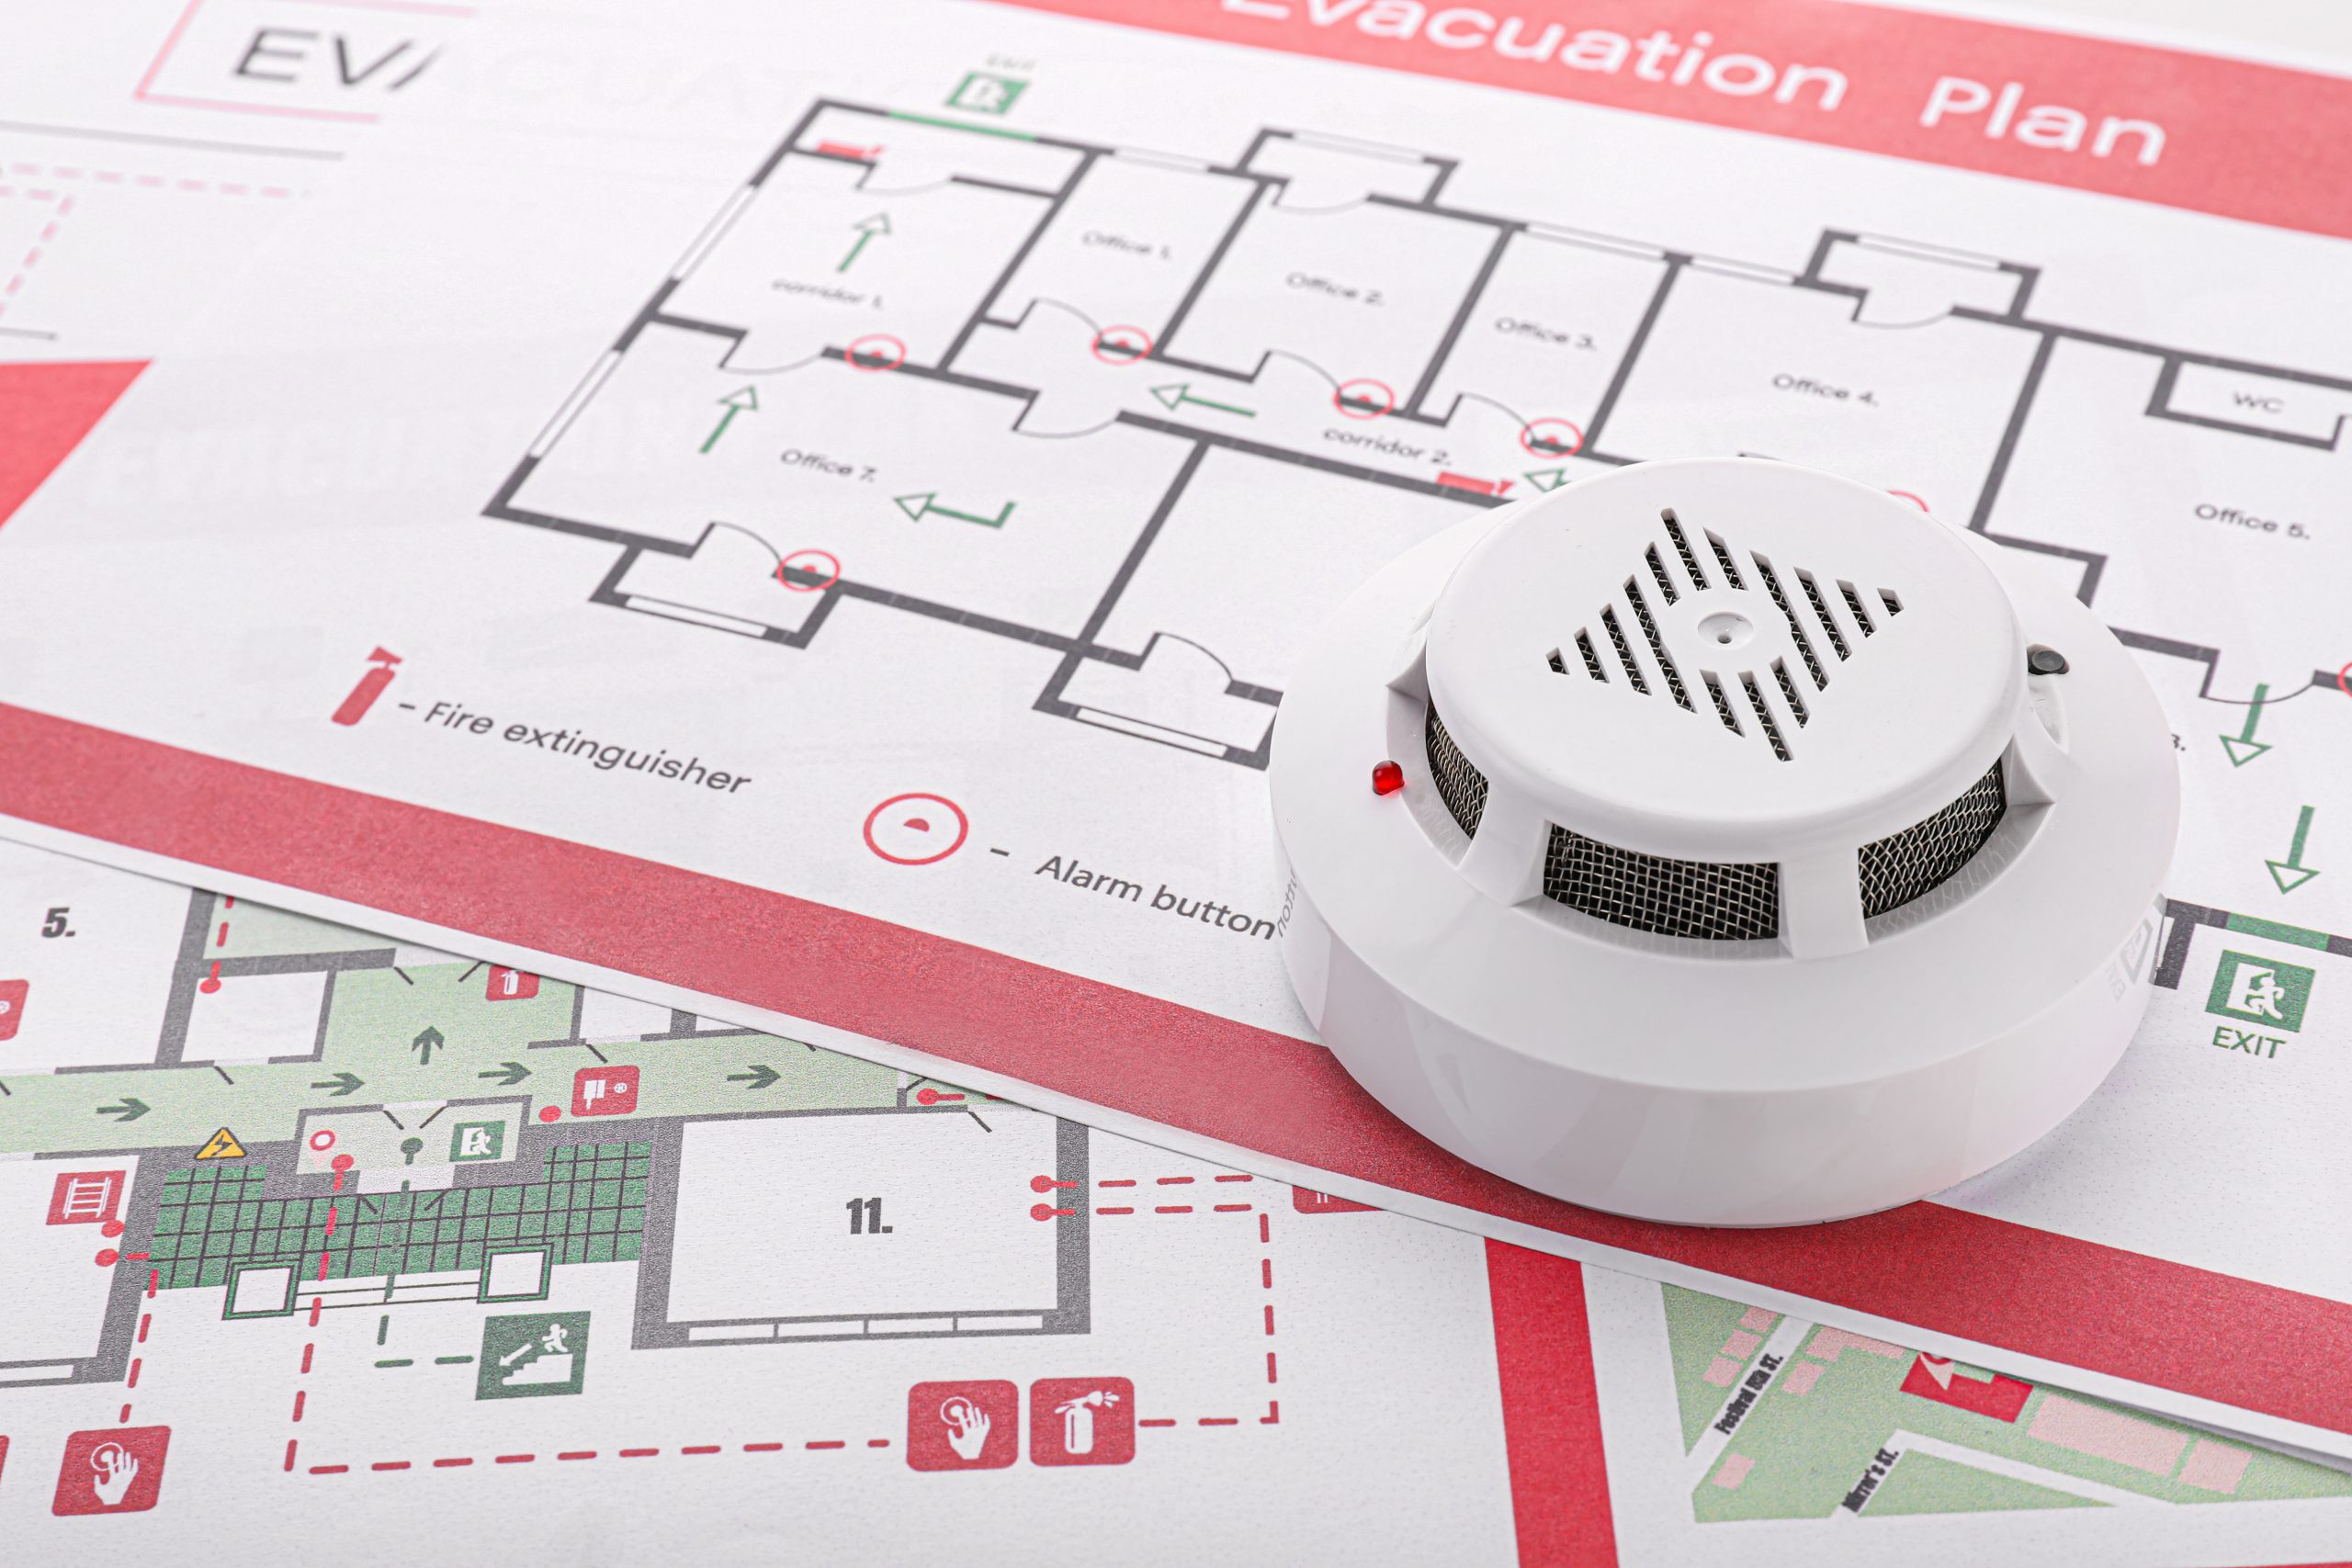
Site layout and access. The plan must encode safe access and egress routes for every credible fire scenario, not just the nearest exit from any given location. For large process areas, this means scenario-specific routing: the safe approach for an emergency responder to a tank fire is not the same as the approach for a heat exchanger fire. Muster point assignments, assembly verification procedures, and accountability systems must be specific enough to work when visibility and communications are degraded.
Saudi Civil Defense Integration: More Than a Notification Protocol
For facilities operating in Saudi Arabia, emergency response planning carries a regulatory dimension that goes beyond NFPA requirements. Saudi Civil Defense is the primary external emergency response authority, and coordination with that authority is not optional — it is a compliance requirement that begins at the design stage, not when an incident occurs.
Effective integration with Saudi Civil Defense requires the facility to maintain current site drawings, fire protection system layouts, and hazardous material inventories in a format accessible to Civil Defense personnel on arrival. It requires pre-established communication protocols, a designated facility emergency coordinator with current contact information registered with the local Civil Defense directorate, and documented access routes for Civil Defense vehicles that account for the facility’s security infrastructure.
Beyond documentation, facilities that conduct joint emergency drills with Saudi Civil Defense — tabletop exercises, functional drills, or full-scale simulations — consistently demonstrate better coordination outcomes when real incidents occur. The drill is not a formality. It is the mechanism by which the plan is stress-tested, gaps are identified, and the two organizations build the operational familiarity that determines how quickly they can work together under pressure.
NFPA 1600, the standard on emergency management and business continuity, provides a framework that complements Saudi Civil Defense requirements. Where the two frameworks address the same area, Saudi Civil Defense requirements govern for facilities operating under Saudi Arabian jurisdiction — but NFPA 1600 is a valuable engineering reference for the internal planning architecture.
Drills, Testing, and Plan Maintenance
An untested ERP is a liability, not an asset. It creates the appearance of preparedness without the substance. The testing program for a process facility ERP must cover three levels of activity:
- Tabletop exercises — scenario-based discussions with key personnel that walk through the ERP decision logic, identify gaps in roles and communications, and surface assumptions that have not been validated. These should be conducted at minimum annually and after any significant process or personnel change.
- Functional drills — partial activations of the ERP that test specific components: the notification and mustering sequence, the ESD initiation procedure, the fire suppression system manual activation. These verify that personnel know their roles and that the systems respond as designed.
- Full-scale exercises — simulated emergency events that activate the complete ERP, including external responder coordination, for a realistic duration. These are resource-intensive but irreplaceable. They expose integration failures that tabletops and functional drills cannot surface.
Plan maintenance must be systematic, not reactive. Every facility modification that affects process streams, fire protection system coverage, staffing structure, or site layout should trigger a formal ERP review. The review should be documented, the revised plan should be distributed to all plan holders, and superseded versions should be retired. A version-controlled ERP with a defined update cycle is a basic engineering discipline that many facilities still do not have in place.
The Bottom Line
Emergency response planning for process facilities is an engineering function. It requires the same rigor, the same integration with physical systems, and the same discipline of testing and update that any other fire protection deliverable demands. A plan that exists only as a document — disconnected from detection logic, suppression sequences, ESD coordination, and Civil Defense protocols — will not perform when it matters.
The facilities that respond effectively to major fire events are not the ones that had the longest plans. They are the ones that engineered their response capability into the facility from the beginning, tested it systematically, and maintained it as their operations evolved. That is not a documentation exercise. It is engineering.
Work With Ignis Sentinel Engineering
Need a fire risk assessment, a third-party plan review, or an NFPA/SAES
compliance check for your facility? Our engineers help Saudi and international
industrial operators design safer operations.